Would you like to learn more about ContractHero?
Want to know how ContractHero can make your contract management more automated and secure? Request a product demo now to get your questions answered and experience the benefits for yourself.


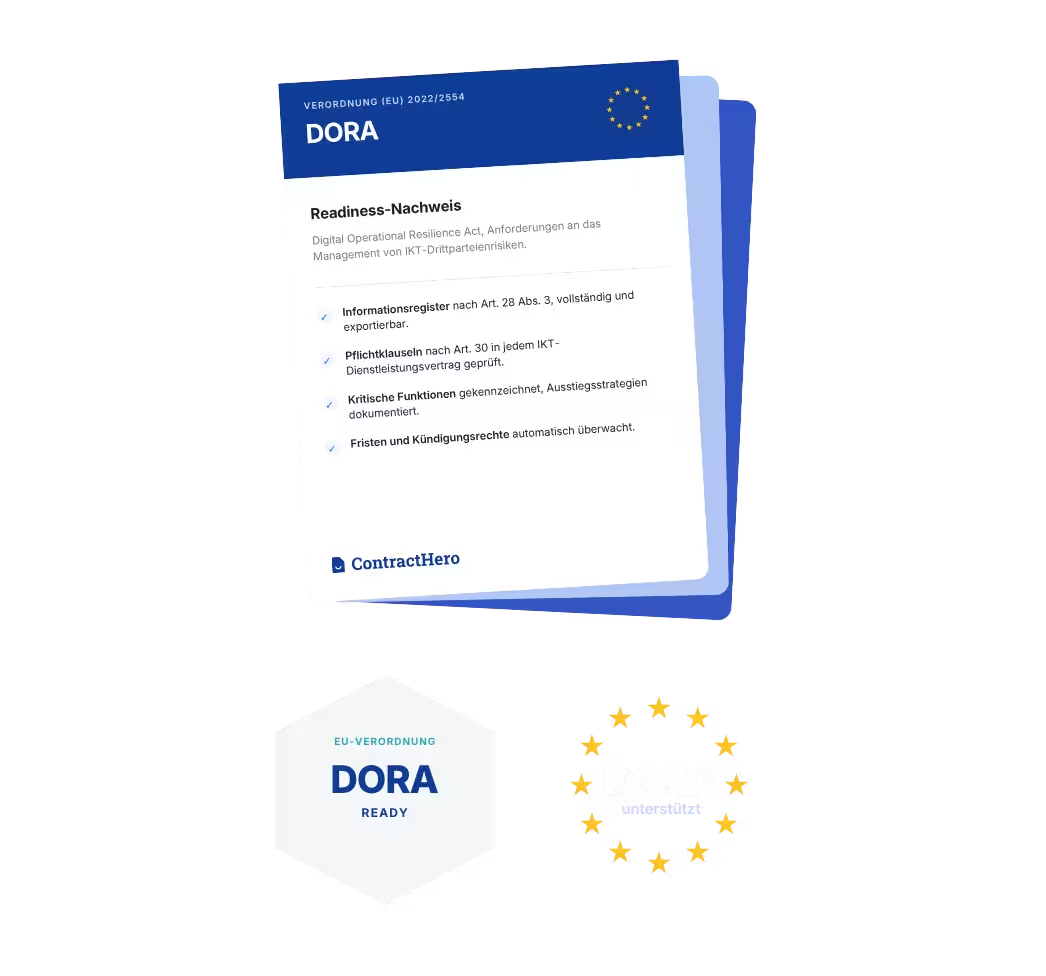
Your contract with a third-party ICT service provider must include the minimum requirements specified in Article 30 of DORA. In addition, you will receive the master data for your information register and the supporting documentation specified in the addendum: an ISO 27001 certificate, summary results of external audits and security tests, and completed security questionnaires.







What sets ContractHero apart from providers who first have to compile the DORA documents.

Performance, information security, ICT incidents, audit rights, subcontractors, termination, and information register. Nine sections based on Articles 28 and 30 of DORA, attached as an appendix to the main contract and signed by both parties.

The ISO 27001 certificate and the complete list of subcontractors are publicly available in the Trust Center. Additional documentation will be provided upon request within 20 business days.

Legal entity, commercial registry number, description of services, processing locations, and subcontractors—all on one page. You can enter the information required under Article 28(3) of DORA instead of having to gather it from various sources.

Regulation (EU) 2022/2554 is mandatory for financial institutions as defined in Article 2. You are responsible for determining whether and to what extent it applies to you.

Because we provide an ICT service to you, we are considered an ICT third-party service provider in this regard. The regulation primarily applies to you, not to us. Our role is to provide you with the basis for compliance.

Processing locations, information security, reporting of ICT incidents, audit rights, subcontractors, and termination must be governed by contract. Our DORA addendum provides precisely these provisions.

You maintain a registry of all third-party ICT service providers and keep it available for your regulatory oversight. We will provide you with the master data for ContractHero on a single sheet.

You decide, based on your internal assessment, whether ContractHero supports a critical or important function as defined in Article 3(22) of DORA. We provide the information, but we do not make the assessment for you.
"Compliance with strict security standards was a key priority for our organization, and ContractHero met these requirements with ease."


“It’s important to have a German provider, because with the certifications that ContractHero has, we’re in a particularly secure position when it comes to storing contract data.”


We currently use 11 subcontractors, all of which have processing locations in the EU or the EEA.
For critical or important functions, we will notify you in advance, and you have the right to object. We require subcontractors to comply with the same DORA-related obligations and remain fully responsible to you. The list in the Trust Center is binding and is continuously updated.

You will determine whether ContractHero supports a critical or important function for you, as defined in Article 3(22) of DORA, based on your internal criticality assessment. We will provide you with the necessary information but will not perform the assessment for you.

Data at rest and in transit is encrypted using AES-256. Access is governed by role-based permissions, and every change is logged. The technical and organizational measures are specified in the data processing agreement.

Backups are performed regularly at data centers in Germany, and the recovery process is tested on a regular basis. Availability, as well as the target values for recovery time and recovery point, are based on a Service Level Agreement (SLA) agreed upon with you, if applicable. You can view the current availability status at any time at status.contracthero.com.

In the event of any conflict between the Addendum and the Main Agreement, the provisions of the Addendum shall take precedence with respect to matters relevant to DORA.
With respect to data protection matters, the Data Processing Agreement shall remain applicable. Any amendments to the Addendum must be made in writing. No liability shall arise beyond the scope of the Main Agreement.
Your IT and legal teams can find the relevant documents in one place, where they are publicly accessible.

Want to know how ContractHero can make your contract management more automated and secure? Request a product demo now to get your questions answered and experience the benefits for yourself.



DORA primarily applies to you as a financial institution, not to us as a software provider. There is no DORA certification for providers. Our role is to provide you with the contractual framework and the supporting documentation you need to comply with Article 30 of DORA and maintain your information register. We have a ready-made addendum for this purpose.
The addendum covers the minimum contractual requirements specified in Art. 30 of DORA: scope of services and classification, processing locations, information security, notification of ICT incidents, access, information, inspection, and audit rights, subcontractors, termination and data return, as well as the master data for your information register. It is an annex to the main contract and is signed by both parties, just like the Data Processing Agreement.
Yes. You will receive a one-page summary sheet listing the legal entity, commercial register number, description of services, processing and storage locations, and the subcontractors used. Important to note: ContractHero does not maintain an LEI; identification is based on the commercial register number HRB 223237. You are responsible for uploading this information to your registry in the specified format.
You may request information and evidence regarding compliance with the addendum; we will respond within 20 business days. This includes the current ISO 27001 certificate, summary results of external audits and security tests, and completed security questionnaires. Your relevant supervisory and resolution authorities, as well as the individuals designated by them, have unrestricted rights of access, information, and inspection, and we cooperate fully with regulatory audits.
In the event of a serious ICT incident or a significant cyber threat affecting you, we will notify you immediately, no later than 24 hours after becoming aware of it. The notification will include the nature and scope of the incident, the data and services affected, the measures taken, and a point of contact. We will assist you with your own reporting obligations under Article 19 of DORA.
The amendment provides for an orderly transition over a 60-day transition period. We will return your data in a standard, structured format and then delete it. This obligation applies to any termination of service, including, specifically, in the event of insolvency, liquidation, or cessation of business operations. The transition will be carried out in such a way that your business operations are not interrupted and your regulatory requirements continue to be met.
Exclusively within the European Union and the EEA. Primary hosting takes place in ISO 27001-certified data centers in Germany; the data does not leave the EU. Data at rest and in transit is encrypted using AES-256, and backups are stored in German data centers. Currently, 11 subcontractors are engaged, all of which have processing locations in the EU or the EEA. Before relocating any processing location, we will notify you with reasonable advance notice and grant you the right to object.

Contract management software for small and medium-sized businesses in Germany, Austria, and Switzerland. Developed and hosted in Germany.